PROACTIVE THREAT DETECTION
Phishing URL not detected by Microsoft Defender
Our SOC team identified this and then launched a check across our customer base to identify any similar exposures.
Business continuity
As a CISO in Quebec, the top priority is to ensure business continuity and mitigate the financial, operational, and reputational risks associated with a security incident. Given the growth and complexity of threats, the security official must choose the right Managed Detection and Response (MDR) service partner to sleep soundly.
The cornerstone of cybersecurity.
Act quickly, but above all, properly.
Evolution at the pace of the attackers
SOLUTION
At Mondata, we recognize that Quebec organizations face significant challenges, including a lack of resources, increasing technological complexity, and high regulatory requirements. To address this, we designed a comprehensive Managed Detection and Response (MDR) service tailored to your local reality, supported by a locally developed platform, which provides optimal detection and response, thereby reducing the impact.
EXPERTISE
Mondata’s strength lies in the efficiency of its experienced, professional, and committed team. With our Security Operations Centre (SOC) continuous monitoring, you benefit from proactive protection, rapid incident response, and the constant sharing of learnings from our field experience.
Phishing URL not detected by Microsoft Defender
Our SOC team identified this and then launched a check across our customer base to identify any similar exposures.
From a malicious file to Flipper Zero
Thanks to a rapid malicious file detection, our team was able to trace the chain of events until it accurately identified the specific USB key that caused the compromise: a Flipper Zero.
Neutralizing a Timebomb
During a war room intervention, our experts identified malware with a deferred payload (Timebomb).
Thanks to our experience, rapid action, and effective coordination with four specialized stakeholders, we enabled the customer to completely neutralize the threat before the execution of the C2 Beacon.
Identified compromise
A customer affected by a compromise could not identify the origin of the incident because their various technologies were not centralized (Defender, Azure, Entra ID, Fortinet, etc.).
Thanks to our unified data lake, we quickly cross-referenced logs from several sources and identified the IP address at the origin of the attack.
PLATFORM
Since 2018, Mondata has made the strategic choice to develop its own platform in Quebec, supporting the Managed Detection and Response service. This positioning enables us to maintain complete technological control and ensure a high degree of agility in response to changing customer needs and the threats they face.
Our platform is built on three fundamental principles designed to adapt to your environments and build a sustainable relationship based on trust, our platform is built on three core principles:
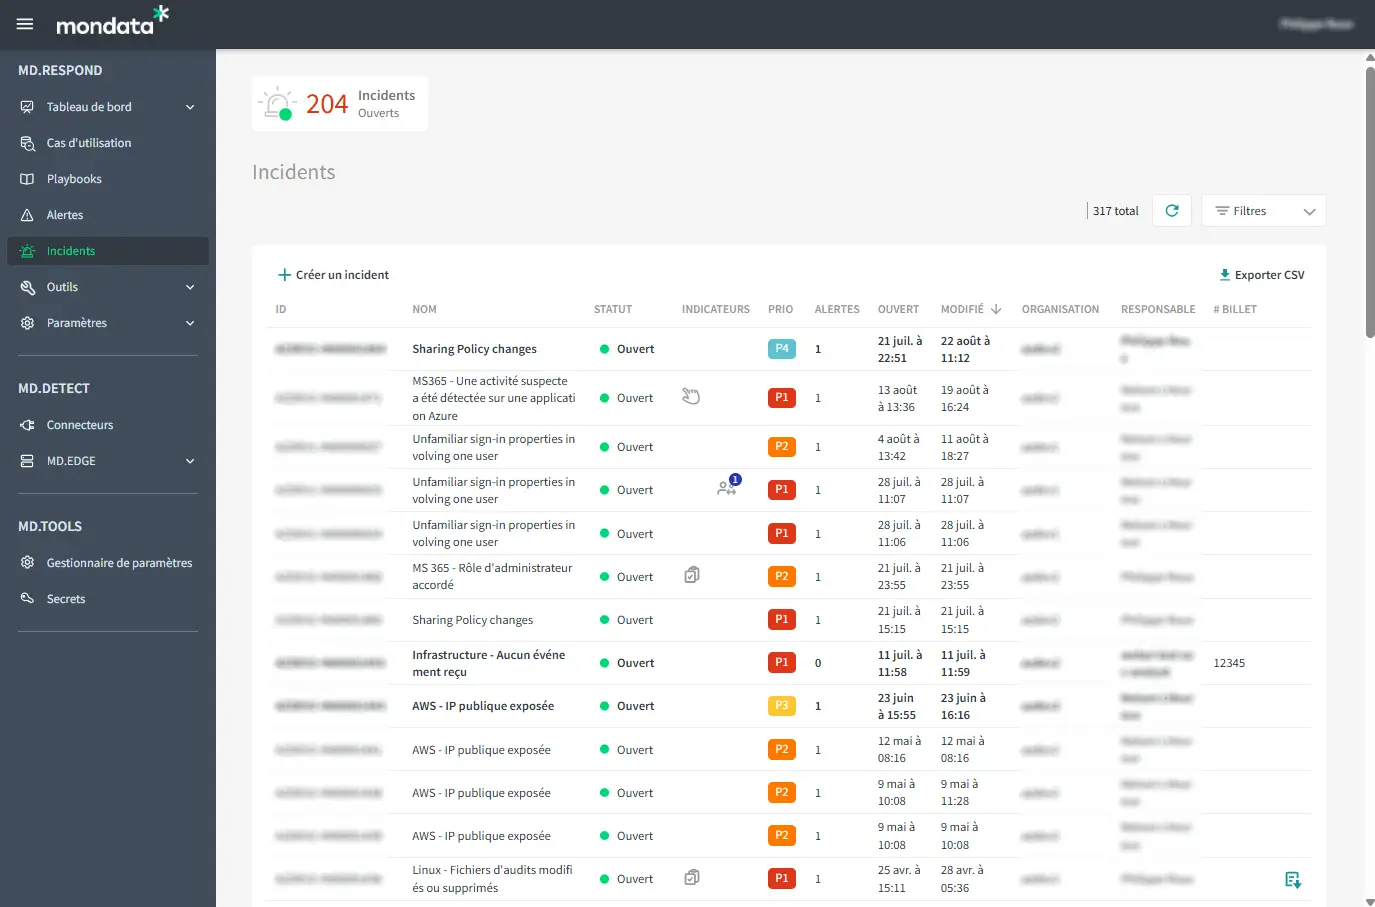
Our platform is compatible with your existing technologies. It centralizes all signals, whether from your workstations, servers, cloud, local, or collaborative environments, into a single data lake, speeding up investigations and interventions.
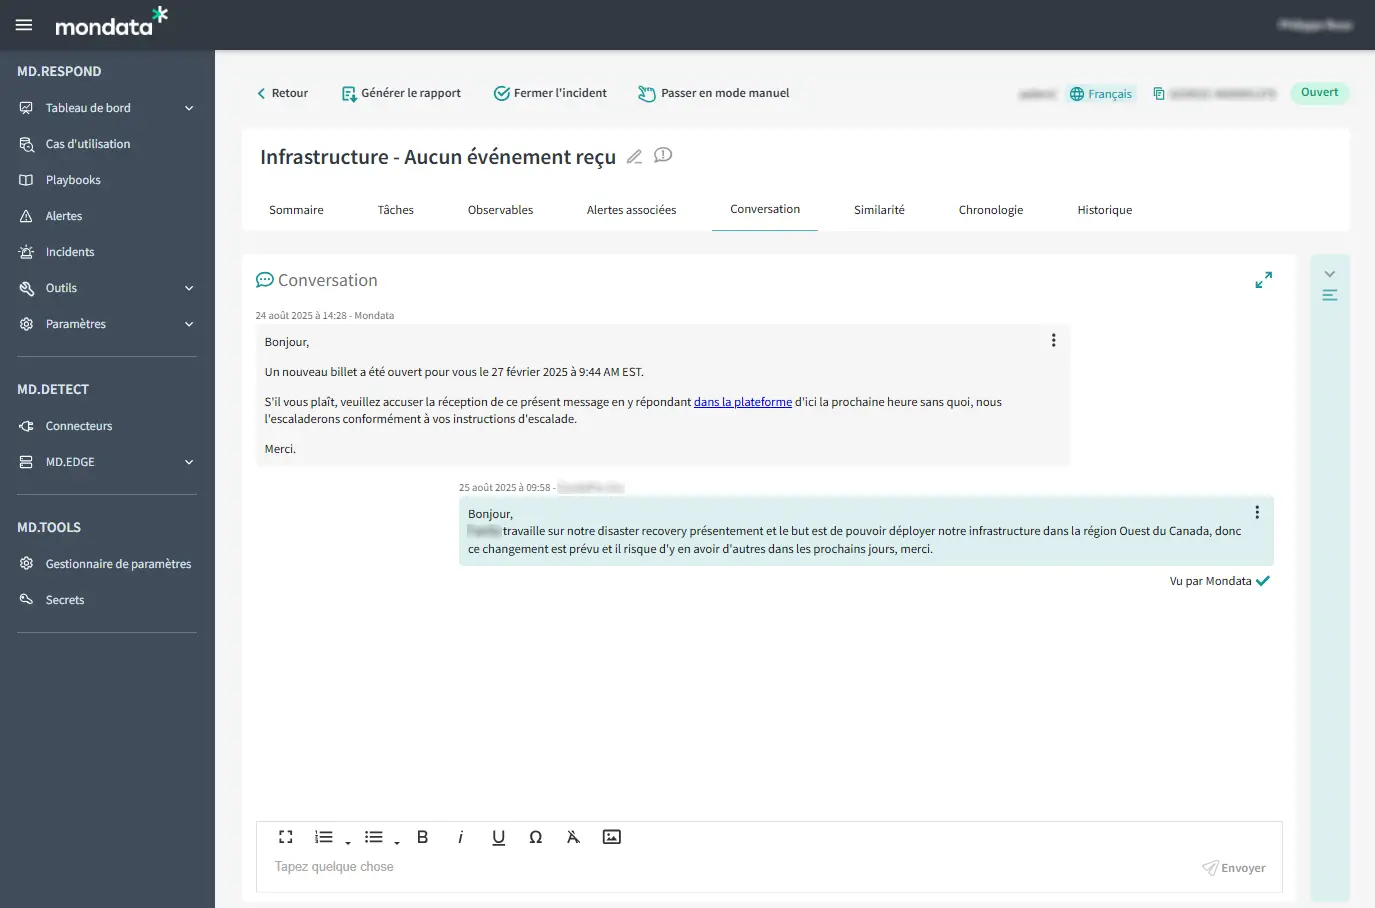
Our solution makes it easier to coordinate responses and collaborate with your teams by providing full visibility on all service components and ongoing security activities, live messaging, and a real-time delegation system.
PARTNERSHIP
We believe that a relationship of trust is built over time, especially before a crisis occurs. Proximity to our customers is at the heart of our approach. Our priority is always to be there to protect your organization and continually strengthen your line of defence.
Our collaborative and human approach is based on three pillars that enable us to increase our effectiveness and sustainably strengthen your cyber resilience significantly: